
1. Local Data Sovereignty and Air-Gapped Execution
Keep sensitive data on-premise to eliminate external breach vectors. Local-first processing ensures that proprietary code, customer records, and intellectual property never leave the host device. This approach satisfies strict data residency laws and reduces the attack surface associated with cloud transmission. By executing models locally, organizations maintain full control over their data lifecycle.
2. Zero Mandatory External Telemetry
3. Immutable Audit Trails for Model Inference
4. Automated Quality Gatekeeping and Validation
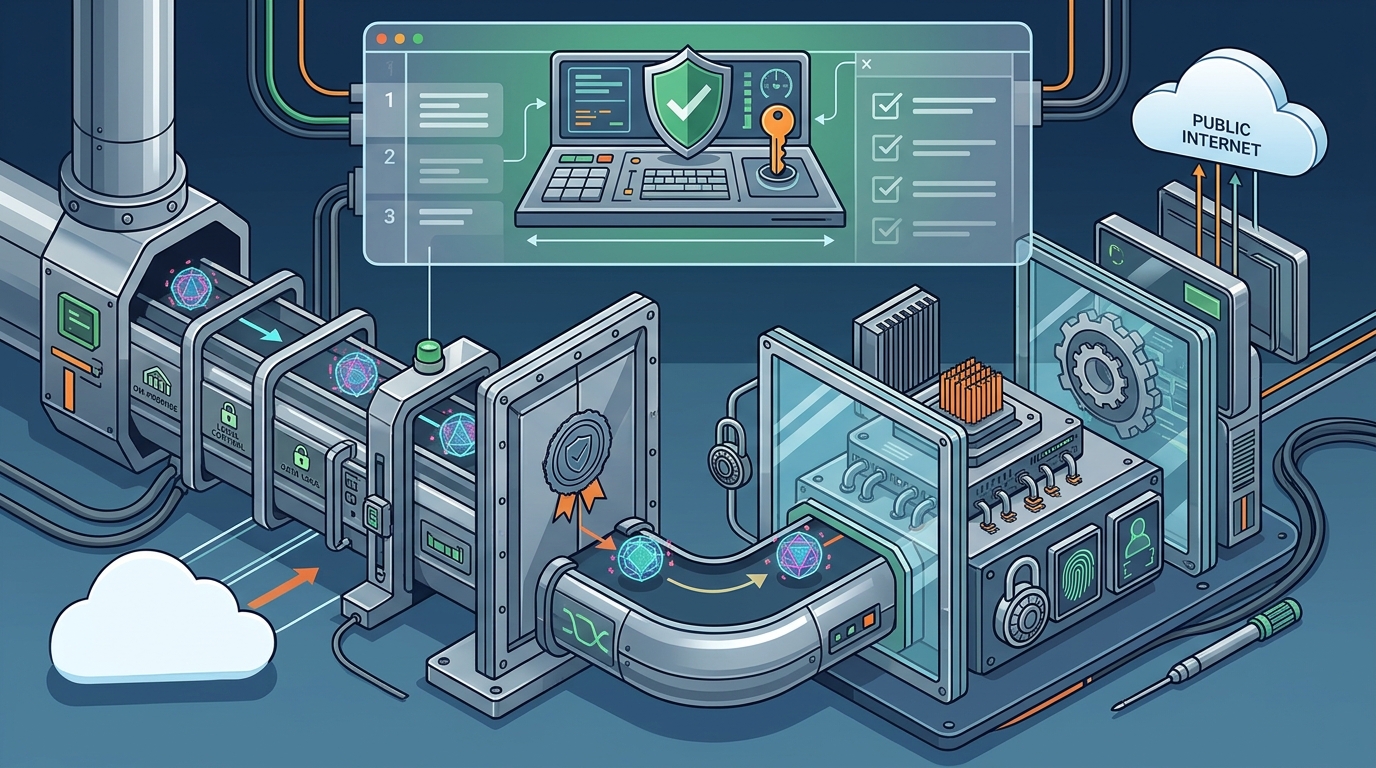
5. Role-Based Access Control for AI Agents
6. Hybrid Escalation with Privacy Preserving Routing
7. Transparent Model Provenance and Licensing
Choosing the Right Governance Framework
Frequently Asked Questions
Does Mahakala.ai send data to the cloud by default?
No. Mahakala.ai operates under a zero-telemetry policy by default. Data remains local unless a user explicitly enables hybrid routing for specific tasks.
How does local-first AI help with GDPR compliance?
Local-first AI helps with GDPR by keeping personal data on-premise. This reduces the risk of data breaches and simplifies data residency requirements.
Can enterprises audit AI decisions made by Mahakala.ai?
What is the difference between local and cloud AI for compliance?
Local AI keeps data on the user's device, offering higher sovereignty. Cloud AI sends data to external servers, which may complicate compliance with strict data privacy laws.
Does multi-agent debate eliminate all AI errors?
No. Multi-agent debate reduces errors through cross-evaluation and quality gatekeeping. It is a validation tool, not a guarantee of perfect accuracy.
Explore how Mahakala.ai secures your enterprise AI workflows. Visit Mahakala.ai to learn more about our sovereign platform. Learn more: mahakalaai com.