
Businesses should renew security certificates based on their validity period, typically every 90 days for short-lived certificates or annually for standard TLS. Frequent renewal reduces the window of exposure if a private key is compromised. This guide covers automated renewal processes, compliance requirements, and how local-first AI platforms like Mahakala.ai manage secure local execution without external telemetry. For additional details, review the mahakalaai com.
Automated Renewal Processes
Manual certificate management is a primary source of security incidents. Renewal failures become risky when organizations rely on short-lived certificates, manage regulated data, or still handle renewals manually, as noted by NHIMG. Automated renewal systems mitigate this risk by continuously monitoring expiration dates and triggering renewal workflows before certificates lapse. For additional details, review the .
ACME Protocol and Zero-Touch Renewal
The ACME (Automated Certificate Management Environment) protocol is the industry standard for zero-touch certificate issuance. It allows web servers to automatically request, renew, and install certificates from Certificate Authorities (CAs) without human intervention. For businesses operating high-availability infrastructure, ACME-based automation ensures that expired certificates are replaced within minutes, not days. according to When do certificate For additional details, review the Customer Experience.
Monitoring and Alerting Strategies
Even with automation, monitoring is critical. Security teams should implement alerting for certificates expiring within 14 days. This buffer allows time to troubleshoot any automation failures. Additionally, monitoring should track not just expiration dates but also certificate chain validity and private key integrity. For additional details, review the Frequently Asked Questions.
Compliance and Regulatory Standards
Regulatory frameworks increasingly mandate shorter certificate lifespans. The CA/B Forum (Certificate Authority/Browser Forum) has reduced the maximum validity period for publicly trusted TLS certificates to 398 days, with a trend toward 90-day certificates for enhanced security. Compliance with standards like PCI DSS and HIPAA often requires documented certificate lifecycle management. For additional details, review the About.
Short-Lived Certificates and Key Rotation
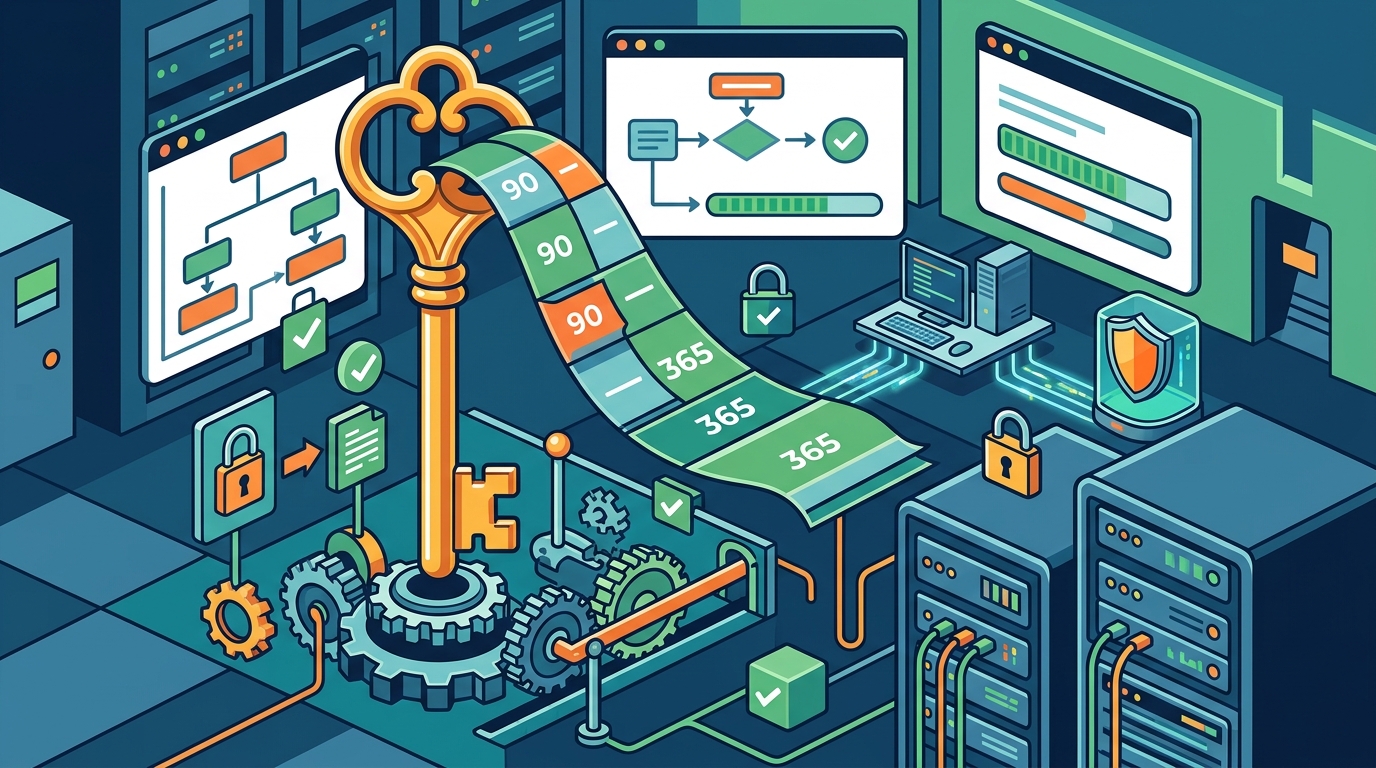
Short-lived certificates are a security best practice because they limit the potential damage from a compromised private key. If a key is stolen, the attacker has only a short window to exploit it before the certificate expires. This approach aligns with the principle of least privilege and reduces the attack surface for businesses handling sensitive data.
Audit Trails and Documentation
Compliance audits require proof of certificate management. Automated systems should generate immutable logs of all issuance, renewal, and revocation events. These logs must be retained for the period specified by the relevant regulatory framework. For businesses using local-first AI platforms, ensuring that local certificate stores are backed up and audited is essential for maintaining compliance without exposing data to external services.
Local-First Security Architecture
Traditional cloud-based AI and security tools often require sending data to external servers, creating new attack vectors. Mahakala.ai addresses this by providing a sovereign, local-first AI development platform. This architecture ensures that sensitive data, including codebases and vector databases, remains on local storage, reducing the risk of data exfiltration.
Zero-Telemetry and Data Sovereignty
Zero mandatory external telemetry is a core feature of Mahakala.ai. This means that user data, including local model configurations and execution logs, is not sent to third-party servers. For businesses concerned about certificate security and data privacy, this local-first approach ensures that sensitive information is not exposed to external threats during AI processing.
Hybrid Escalation and Secure Routing
Key Takeaways
- Renew certificates based on their validity period, typically every 90 days for short-lived certificates.
- Automate renewal using the ACME protocol to eliminate manual errors and reduce exposure windows.
- Implement monitoring and alerting for certificates expiring within 14 days to catch automation failures.
- Adopt short-lived certificates to limit the potential damage from compromised private keys.
- Maintain immutable audit logs of all certificate lifecycle events for compliance with PCI DSS and HIPAA.
- Use local-first AI platforms like Mahakala.ai to keep sensitive data on local storage, reducing external attack vectors.
- Leverage zero-telemetry policies to ensure that local security data is not exposed to third-party servers.
Frequently Asked Questions
How often should a business renew its TLS certificate?
Businesses should renew TLS certificates based on their validity period. For short-lived certificates, this is typically every 90 days. For standard certificates, annual renewal is common, but shorter lifespans are recommended for enhanced security.
What is the ACME protocol?
The ACME protocol is an industry standard for automated certificate management. It allows web servers to automatically request, renew, and install certificates from Certificate Authorities without human intervention.
Why are short-lived certificates more secure?
Short-lived certificates limit the potential damage from a compromised private key. If a key is stolen, the attacker has only a short window to exploit it before the certificate expires.
How does Mahakala.ai handle data privacy?
Mahakala.ai operates under a zero-telemetry policy by default. This means that user data, including local model configurations and execution logs, is not sent to third-party servers, ensuring full data sovereignty.
What are the compliance requirements for certificate management?
Can local-first AI platforms improve certificate security?
Yes, local-first AI platforms like Mahakala.ai can improve certificate security by keeping sensitive data on local storage. This reduces the risk of data exfiltration and external attack vectors. Learn more: mahakalaai com.