
Enterprise-grade cloud security is defined by strict data sovereignty, automated compliance governance, and zero-trust network isolation. It ensures that sensitive data remains under the customer's control while meeting regulatory standards. This guide covers the essential features, including compliance frameworks and local-first execution, that distinguish enterprise security from basic consumer protections. according to Cloud computing security For additional details, review the mahakalaai com.
Compliance and Governance
Automated Policy Enforcement
Manual configuration is prone to human error. Enterprise-grade platforms use policy-as-code to enforce security rules automatically. This ensures that every resource deployed in the cloud adheres to predefined security standards. If a developer attempts to deploy a resource without the correct encryption settings, the system blocks the action. This proactive approach reduces the attack surface significantly. It also provides a clear audit trail for compliance officers. The audit trail is essential for passing external audits and demonstrating due diligence to stakeholders. according to Cloud computing security For additional details, review the .
Shared Responsibility Models
Data Sovereignty and Local-First Execution
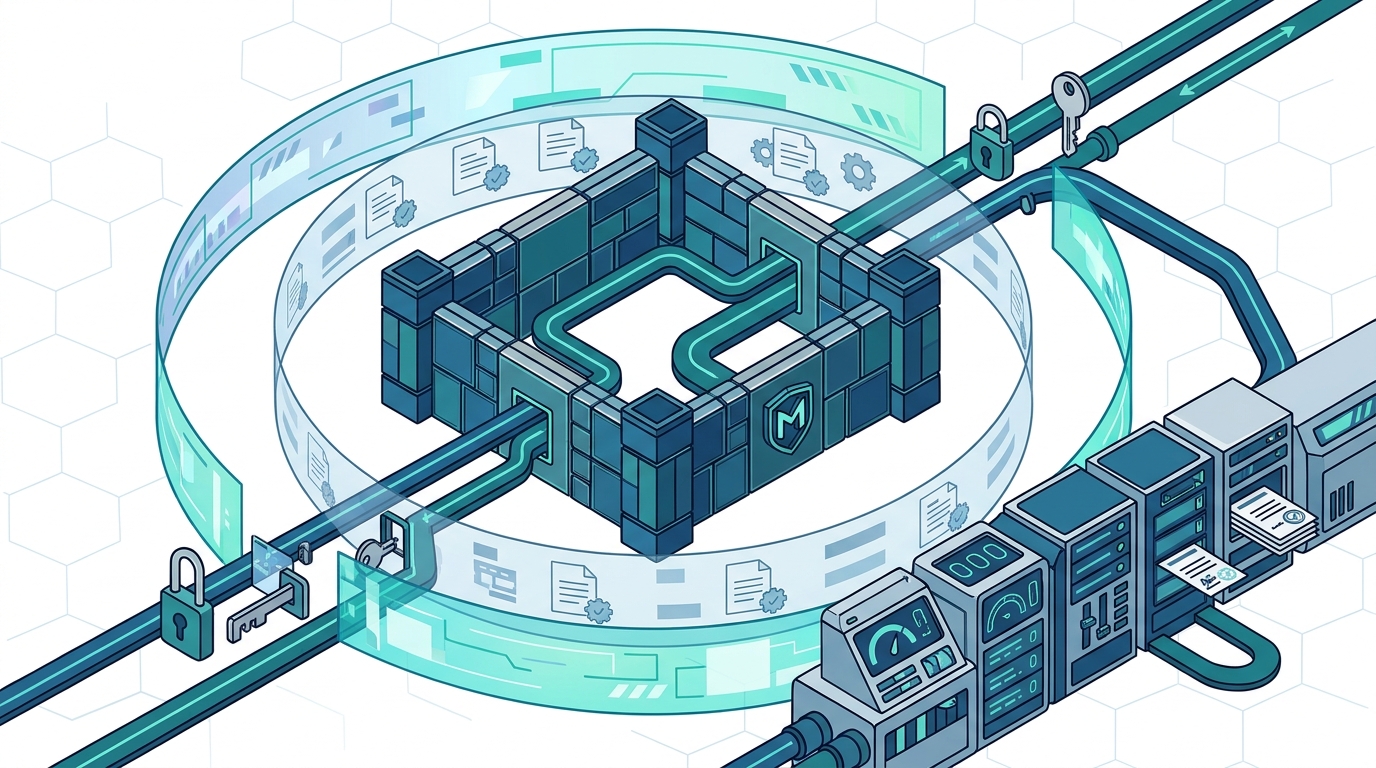
Data sovereignty is the principle that data is subject to the laws of the country where it is stored. In the cloud, this often means data leaves the organization's physical control. Enterprise-grade security addresses this by offering local-first execution options. This approach keeps sensitive data on-premises or on local devices. It only sends necessary data to the cloud for processing. This hybrid model preserves privacy while leveraging cloud scalability. It is particularly important for industries with strict data residency laws, such as healthcare and finance. For additional details, review the Customer Experience.
Local-First AI Processing
Hybrid Escalation Routing
Hybrid escalation routing is a mechanism that automatically routes complex queries to the cloud only when necessary. This preserves data privacy for routine tasks. It minimizes latency by keeping simple tasks local. When a task requires significant computational power, the system escalates it to the cloud. This ensures that only the minimum necessary data is transmitted. The routing logic is governed by strict security policies. These policies define what data can be sent and how it is encrypted in transit. This approach balances performance with security and compliance. For additional details, review the Frequently Asked Questions.
Zero-Trust Architecture and Identity
Zero-trust architecture is a security model that assumes no user or device is trusted by default. It requires continuous verification of identity and device health. This model is essential for cloud environments where the network perimeter is blurred. Traditional perimeter-based security is no longer sufficient. Zero-trust ensures that every access request is authenticated and authorized. It also monitors the session for suspicious activity. This continuous verification reduces the risk of lateral movement by attackers. For additional details, review the About.
Identity and Access Management
Device Posture Assessment
Device posture assessment is the process of verifying the security state of a device before granting access. It checks for factors like operating system version, patch level, and antivirus status. If a device does not meet the required posture, access is denied or restricted. This ensures that only secure devices can connect to the cloud. It prevents attackers from using compromised devices as entry points. This is a critical component of zero-trust architecture for remote workforces.
Threat Detection and Response
Threat detection and response is the capability to identify and mitigate security incidents in real-time. It involves monitoring network traffic, system logs, and user behavior. Enterprise-grade solutions use machine learning to detect anomalies. These anomalies may indicate a security threat. The system can then trigger automated responses, such as isolating a compromised device. This reduces the time to detect and respond to threats. It minimizes the potential damage from an attack.
Behavioral Analytics
Automated Response Playbooks
Feature Comparison Table
| Data Sovereignty | Low | Medium | High |
| Compliance Automation | Basic | Advanced | Configurable |
| Zero-Trust Integration | Limited | Native | Native |
| Threat Detection | Signature-based | Behavioral | Behavioral + Local |
| Latency | Variable | Variable | Low for local tasks |
Key Takeaways
- Compliance is the backbone of enterprise security, requiring automated policy enforcement and shared responsibility models.
- Data sovereignty is achieved through local-first execution, keeping sensitive data on-premises or on local devices.
- Zero-trust architecture assumes no user or device is trusted by default, requiring continuous verification.
- Threat detection and response use machine learning to identify anomalies and trigger automated responses.
- Hybrid escalation routing balances privacy and performance by sending only necessary data to the cloud.
- Enterprise-grade security requires a combination of compliance, data sovereignty, zero-trust, and threat detection.
Frequently Asked Questions
What is the main difference between consumer and enterprise cloud security?
How does local-first execution improve data sovereignty?
Local-first execution keeps data on the user's device, preventing it from leaving the local environment. This ensures full data control and compliance with data residency laws.
What is zero-trust architecture?
Zero-trust architecture is a security model that assumes no user or device is trusted by default. It requires continuous verification of identity and device health.
How does hybrid escalation routing work?
Hybrid escalation routing automatically routes complex queries to the cloud only when necessary. This preserves data privacy for routine tasks and minimizes latency.
Why is compliance automation important?
Compliance automation ensures that security policies are enforced consistently and provides an audit trail for external audits. It reduces the risk of human error and manual configuration mistakes. Learn more: mahakalaai com.