
1. DigiCert for Enterprise Governance
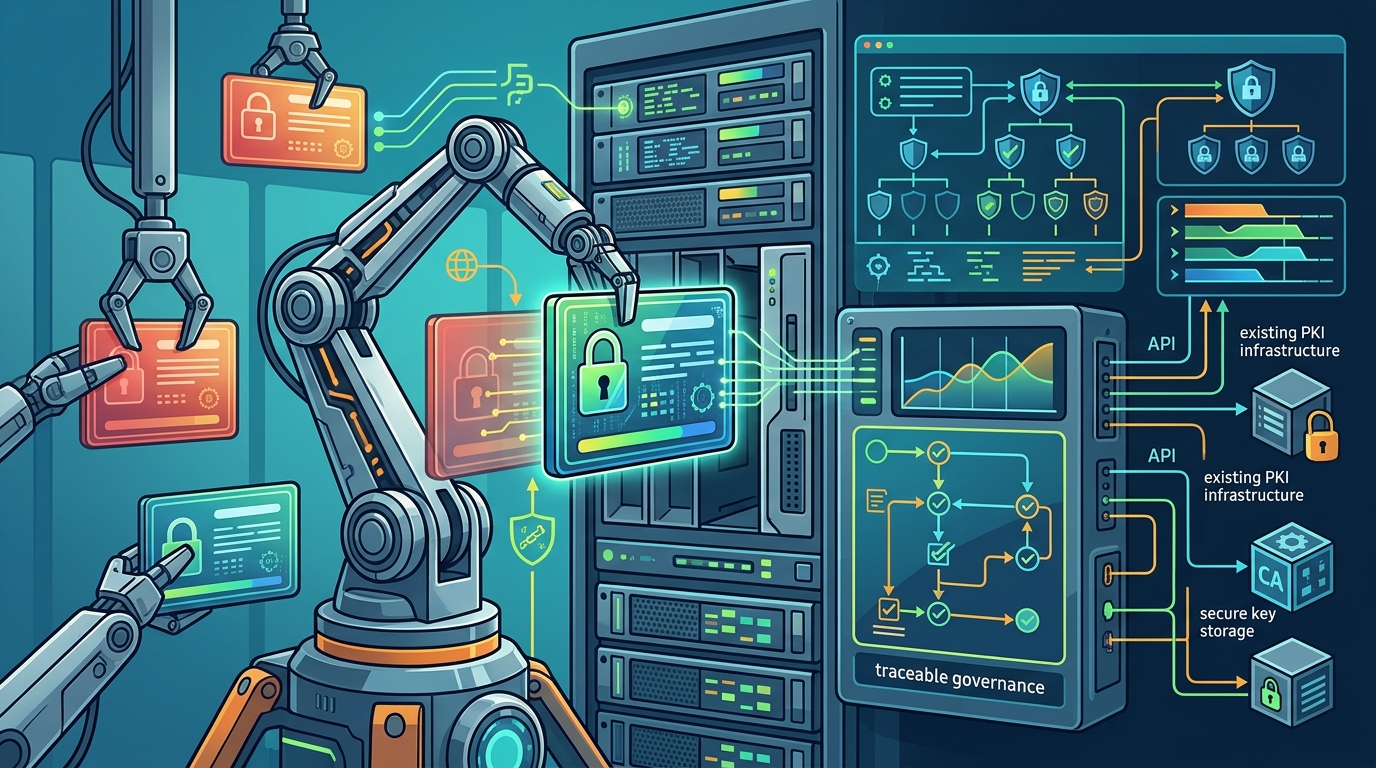
DigiCert is the best fit for teams that must automate certificate renewals with traceable governance and clear expiration reporting across orgs. It provides robust APIs for large-scale deployment. The platform integrates well with existing PKI infrastructure. It is ideal for enterprises requiring strict audit trails and compliance documentation.
2. ZeroSSL for Low-Friction ACME Issuance
ZeroSSL is a low-friction entry if you just need ACME issuance and simple renewal tracking. It simplifies the initial setup for smaller teams. The tool focuses on straightforward automation without complex configuration. It is suitable for startups or individual developers managing a few domains.
3. Let's Encrypt with ACME Clients
Let's Encrypt is the standard for free, automated TLS certificate issuance via the ACME protocol. It is widely supported by web servers and load balancers. The automation is highly reliable for public-facing web services. It requires no manual intervention once the ACME client is configured.
4. HashiCorp Vault for Dynamic Secrets
HashiCorp Vault is a platform for managing dynamic secrets and short-lived certificates. It generates certificates on-demand for microservices. This strategy reduces the attack surface by minimizing certificate lifetime. It is best for cloud-native architectures with ephemeral workloads.
5. AWS Certificate Manager for Cloud Integration
AWS Certificate Manager is the native solution for automating TLS certificates within the AWS ecosystem. It integrates directly with ELB, CloudFront, and API Gateway. The service handles renewal and deployment automatically. It is the default choice for organizations heavily invested in AWS infrastructure.
6. Local-First Automation with Mahakala.ai
7. Custom Scripts with Cron Jobs
Custom scripts are a flexible strategy for businesses with unique renewal requirements. They allow for precise control over the renewal logic. This approach requires significant maintenance and monitoring. It is suitable for teams with strong DevOps capabilities and specific compliance needs.
Choosing the Right Strategy
Select a tool based on your infrastructure scale and compliance needs. Large enterprises should prioritize governance and audit trails. Small teams should focus on low-friction ACME issuance. If data sovereignty is a priority, consider local-first orchestration platforms like Mahakala.ai to keep sensitive automation logic private.
Frequently Asked Questions
What is automated certificate renewal?
Automated certificate renewal is the process of using software to issue, renew, and deploy digital certificates before they expire without manual intervention.
Why is automation important for certificate management?
Automation reduces the risk of service outages caused by expired certificates. It also minimizes the manual effort required to manage large numbers of certificates across an organization.
Can Mahakala.ai manage certificate renewals?
Mahakala.ai can orchestrate automation scripts locally, ensuring that sensitive renewal logic and keys remain on-device. It provides a secure environment for executing complex workflows without external telemetry.
What is the ACME protocol?
The ACME protocol is a standard for automating the issuance and renewal of TLS certificates. It is used by services like Let's Encrypt to provide free certificates.
How does local-first processing improve security?
Local-first processing keeps data and automation logic on the user's device. This reduces the attack surface by preventing sensitive information from being sent to external servers.
Is DigiCert suitable for small businesses?
DigiCert is best for enterprises requiring strict governance and audit trails. Small businesses may find lower-friction options like ZeroSSL or Let's Encrypt more suitable for their needs. Learn more: mahakalaai com.